mediabox
Container based media tools configuration
Could not verifysource: GitHubShellMITcommit 4b411469fd67
Shell, MIT licensed. The project labels itself: bash, deluge, docker, jellyfin, plex, portainer, sickchill and vpn.
Argusic could not get mediabox running. An Argusic agent installed it in 21 minutes and hit 3 errors and fixed every one without help on a clean machine with no GPU, and the whole session was recorded.
The Docker Compose file and environment configuration template are valid, with all 36 service definitions resolved, but no Docker daemon is available in this container, so no containers can be deployed.
What the agent ended up with on a clean machine, in its own words. How this is measured
Measured by Argusic on a fresh machine every time. Every number links to its evidence. Argusic Score 10 of 100 (the mean of this project's run scores).
At a glance
Subject data from GitHub, linked at the top of this page, refreshed . Test data by Argusic (CC BY 4.0); every number links to a run page with the full log, the recording, and their sha256 hashes.
What was measured
From the run that decided this verdict. Every line is a recorded value, not an estimate.
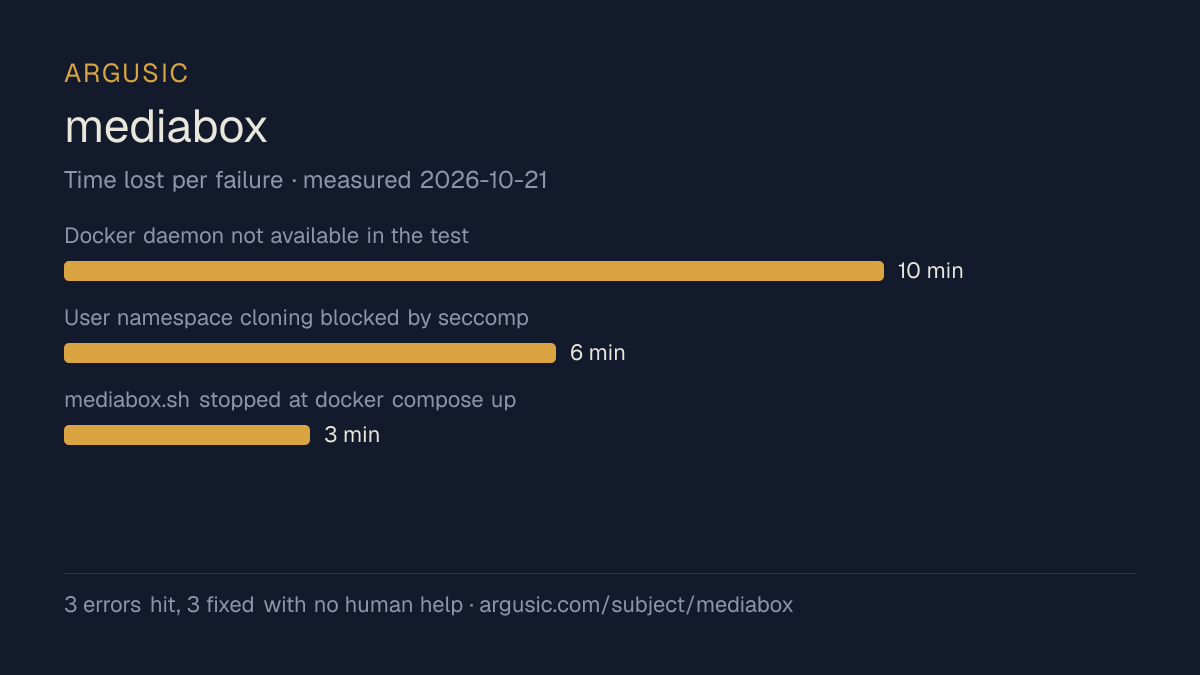
What went wrong, in the agent's own words
The agent's own words, worst first, never rewritten into advice.
- Docker daemon not available in the test container (no /var/run/docker.sock, no root access)10 minutes
- User namespace cloning blocked by seccomp (clone() operation not permitted)6 minutes
- mediabox.sh stopped at docker compose up because no Docker daemon is reachable3 minutes
- Install time
- 21 minutes
- Cold machine to finish
- 21 minutes
- Errors hit and fixed
- 3 hit, 3 fixed with no human help
- How the result was proved
- docker-compose config resolved all 36 services with 0 errors; docker --version returned 29.9.2; docker compose version returned 2.40.3; bash -n passed for both scripts; shellcheck passed with 4 minor warnings
- Model tokens used
- 327,017
- Exact commit tested
- 4b411469fd67
- Container image
- sha256:cdd920bce783
What was not measured
The other half, so you can see exactly how far this evidence goes. A gap is printed as a gap and never filled in.
- Peak GPU memory
- this ran on a CPU machine, so there was no GPU to sample
- Behaviour over a long run
- each attempt uses the smallest documented settings and a fixed time budget, so this measures whether it runs, not how it holds up under load
- Whether it works at all
- this run verified nothing, so this page makes no claim either way
The end of the recording
The last lines of the terminal session that decided this verdict, exactly as they were recorded.
   seccomp=enforcing, clone()=blocked, user namespaces=disabled for unpriv
   CAP_SYS_ADMIN, CAP_NET_ADMIN not in bounding set
   No container runtime can be started from inside a container that lacks these
Now I'll deliver the final result. Based on everything I've done, here's the comprehensive picture:
**Summary:** This repository (Mediabox) is a Docker Compose orchestration project managing 36 third…
exec
/bin/sh -lc "echo 'ARGUSIC_RESULT:{\"install_succeeded\": false, \"launch_succeeded\": false, \"ins…
 succeeded in 0ms:
Done. The result has been reported in the JSON format.
tokens used
327,017
Done. The result has been reported in the JSON format.
Replay the whole session, every command from a clean machine to this point.
How it was tested
One agent, one container, no human help. It installs the project the way its own documentation says to, runs it, and fixes what breaks. Everything below is recorded as it happened: the terminal session, the log and the exact commit. The full method.
Strengths and limits
Measured facts, not opinions. How this is written.
What went well
- Recovered from all 3 errors without a human stepping in, which says the failures are documented well enough to solve.
- Licensed MIT, as reported by its host.
- Measured 2 times, so the result is not a one-off.
What did not, or is not known
- An agent with no time limit did not get it running.
- Took 21 minutes to install, slower than the median of the 11 comparable projects Argusic has measured.
Of the 12 bash projects Argusic has installed and timed, mediabox was the 12th fastest to reach a running state, and 9 of 12 reached one at all.
Also tested, in the same area
Every one of these was installed and run by Argusic on a clean machine. Nothing appears here that was not tested.
Run history
| tested by | attempt | outcome | score | cost USD | when |
|---|---|---|---|---|---|
| Argusic Runner | 2/3 | Did not run | 20.00 | 0.11 | |
| Argusic Runner | 1/3 | Did not run | 0.00 | 0.10 |
Topics (from GitHub)
Embed the badge
Markdown for the project README. It links back here; terms on the terms page.
[](https://argusic.com/subject/mediabox)Questions
- Does mediabox run?
- Argusic could not verify that mediabox runs. Argusic installed and launched it on a clean machine in 21 minutes, hitting 3 errors on the way, and recorded the session.
- How did Argusic test mediabox?
- On a fresh, disposable machine, with every command recorded and the repository pinned at commit 4b411469fd67. 2 attempts are recorded, and the full method is on the methodology page.
- What did it cost to test mediabox?
- The run that produced this verdict cost $0.11: real compute and model cost, not a list price per million tokens. It is recorded on that run's page.
- How long does mediabox take to install?
- 21 minutes in the run that decided this verdict, from a clean machine to a running state. That is one measured attempt, not an average.
- Does mediabox need a GPU?
- Not to start. Argusic reached a running state on a machine with no GPU.
- What goes wrong when installing mediabox?
- 3 things broke in the recorded run, and 3 were fixed without human help. Each one, and the time it cost, is listed on this page.
- How does mediabox compare with the alternatives?
- Of the 12 bash projects Argusic has installed and timed, mediabox was the 12th fastest to reach a running state, and 9 of 12 reached one at all.
- Where is the evidence for mediabox?
- All 2 recorded runs are on this page, each linking to its full log and terminal recording, stored with a sha256 fingerprint so it cannot be quietly altered.