wireguard-docs
📖 Unofficial WireGuard Documentation: Setup, Usage, Configuration, and full example setups for VPNs supporting both servers & roaming clients.
Runssource: GitHubhomepageShellMITcommit f87afb4f646d
Shell, MIT licensed. The project labels itself: internet, kernel module, linux, mesh networking, nat, networking, security and tunnel.
wireguard-docs runs. An Argusic agent installed it in 45 minutes and hit 6 errors and fixed every one without help on a clean machine with no GPU, and the whole session was recorded.
The repo's example start.sh/stop.sh scripts run successfully on the container's built-in kernel WireGuard (built wg/ip toolchain in /tmp/wgtools), establishing real encrypted tunnels and passing TCP echo traffic across the example-simple-server-to-server, example-simple-client-to-server, example-internet-browsing-vpn, example-full, and example-lan-briding configs, with stop.sh cleanly removing all wg interfaces;
What the agent ended up with on a clean machine, in its own words. How this is measured
Measured by Argusic on a fresh machine every time. Every number links to its evidence. Argusic Score 90 of 100 (the mean of this project's run scores).
At a glance
Subject data from GitHub, linked at the top of this page, refreshed . Test data by Argusic (CC BY 4.0); every number links to a run page with the full log, the recording, and their sha256 hashes.
What was measured
From the run that decided this verdict. Every line is a recorded value, not an estimate.
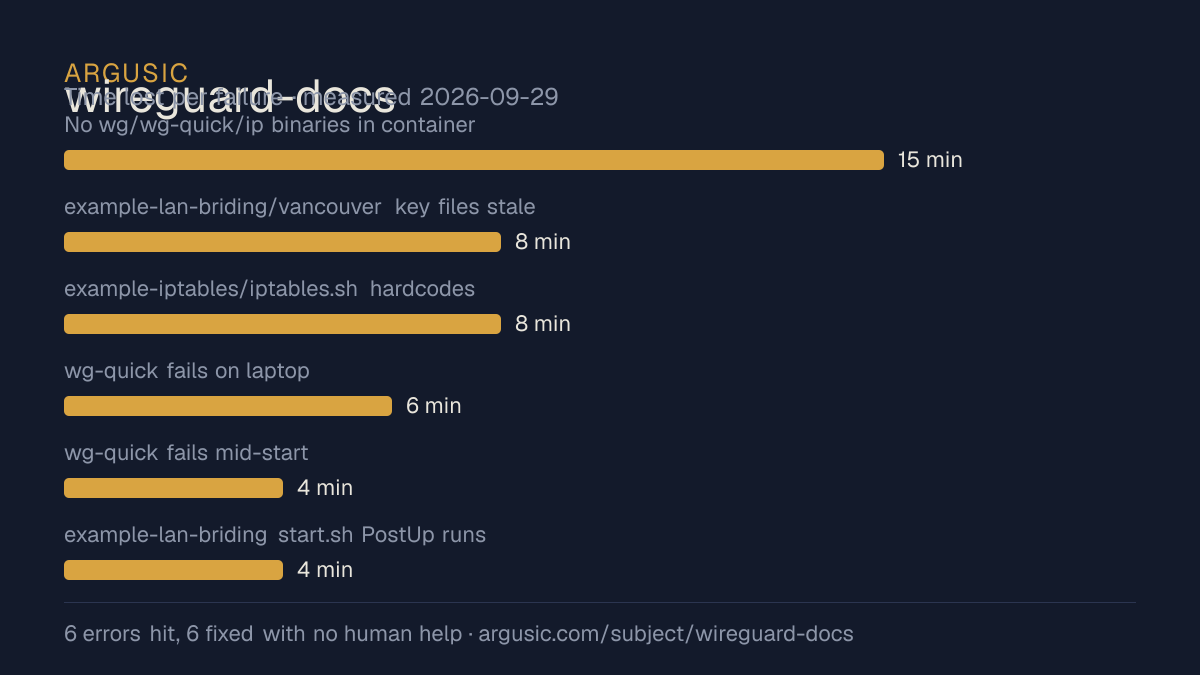
What went wrong, in the agent's own words
The agent's own words, worst first, never rewritten into advice.
- No wg/wg-quick/ip binaries in container (non-root, no apt install possible)15 minutes
- example-lan-briding/vancouver key files stale: vancouver.key held the shared server1 private key 2P/3ll... and vancouver.key.pub held q/+jw... which did not match, while vancouver/wg0.conf and all peer references use WN+bvd.../8bSk5f...8 minutes
- example-iptables/iptables.sh hardcodes /sbin/iptables which does not exist here; scripts has no install path and netfilter is unavailable in this container8 minutes
- wg-quick fails on laptop (AllowedIPs 0.0.0.0/0): ip6tables-restore and iptables-restore missing6 minutes
- wg-quick fails mid-start: resolvconf missing (DNS= lines)4 minutes
- example-lan-briding start.sh PostUp runs iptables, not installed in container4 minutes
- Install time
- 45 minutes
- Cold machine to finish
- 30 minutes
- Errors hit and fixed
- 6 hit, 6 fixed with no human help
- How the result was proved
- unshare -Urn bash run_two_node_auto.py: TCP echo client on server1 returned 'ECHO:HELLO-VIA-REPO' from 10.0.44.2 with latest handshake: Now and 180B/92B transfer on both wg show outputs; stop.sh removed wg0 (0 links left); lan mesh: all 6 'ECHO:HELLO-MESH' ok; full hub: laptop and home-server 'ECHO:HELLO-VIA-HUB'; wireguard-tools wg --version printed v1.0.20210914
- Model tokens used
- 1,553,604
- Exact commit tested
- f87afb4f646d
- Container image
- sha256:cdd920bce783
What was not measured
The other half, so you can see exactly how far this evidence goes. A gap is printed as a gap and never filled in.
- Peak GPU memory
- this ran on a CPU machine, so there was no GPU to sample
- Behaviour over a long run
- each attempt uses the smallest documented settings and a fixed time budget, so this measures whether it runs, not how it holds up under load
The end of the recording
The last lines of the terminal session that decided this verdict, exactly as they were recorded.
- Remaining gap (not fixable without root): `example-iptables/iptables.sh` hardcodes `/sbin/iptable…
The single-line machine-readable result is printed above (`ARGUSIC_RESULT: {...}`).
tokens used
1,553,604
The task is complete. Final summary of what was done:
**Work performed**
- Read the README/docs: this is the wireguard-docs repo (unofficial WireGuard documentation with 5 …
- Standard install wasn't possible directly (non-root, no `wg`/`wg-quick`/`ip`), so I built the off…
- Diagnosed and fixed each error, including a genuine repo bug: `example-lan-briding/vancouver` had…
- Verified real behavior end-to-end: ran the repo's own `start.sh` scripts with the real kernel Wir…
- Remaining gap (not fixable without root): `example-iptables/iptables.sh` hardcodes `/sbin/iptable…
The single-line machine-readable result is printed above (`ARGUSIC_RESULT: {...}`).
Replay the whole session, every command from a clean machine to this point.
How it was tested
One agent, one container, no human help. It installs the project the way its own documentation says to, runs it, and fixes what breaks. Everything below is recorded as it happened: the terminal session, the log and the exact commit. The full method.
Strengths and limits
Measured facts, not opinions. How this is written.
What went well
- Reached a running state on a clean machine, with the session recorded.
- Installed in 45 minutes.
- Recovered from all 6 errors without a human stepping in, which says the failures are documented well enough to solve.
- Ran without a GPU, so it does not need one to start.
- Licensed MIT, as reported by its host.
- Measured 2 times, so the result is not a one-off.
What it is a reasonable choice for
- Trying it on a laptop or a small server: it reached a running state without a GPU.
Also tested, in the same area
Every one of these was installed and run by Argusic on a clean machine. Nothing appears here that was not tested.
Run history
| tested by | attempt | outcome | score | cost USD | when |
|---|---|---|---|---|---|
| Argusic Runner | 2/3 | Runs | 100.00 | 0.32 | |
| Argusic Runner | 1/3 | Unverified | 80.00 | 0.10 |
Topics (from GitHub)
internetkernel-modulelinuxmesh-networkingnatnetworkingsecuritytunneltuntapudpvpnvpn-solutionwireguard
Embed the badge
Markdown for the project README. It links back here; terms on the terms page.
[](https://argusic.com/subject/wireguard-docs)Questions
- Does wireguard-docs run?
- Yes. wireguard-docs runs. Argusic installed and launched it on a clean machine in 45 minutes, hitting 6 errors on the way, and recorded the session.
- How did Argusic test wireguard-docs?
- On a fresh, disposable machine, with every command recorded and the repository pinned at commit f87afb4f646d. 2 attempts are recorded, and the full method is on the methodology page.
- What did it cost to test wireguard-docs?
- The run that produced this verdict cost $0.32: real compute and model cost, not a list price per million tokens. It is recorded on that run's page.
- How long does wireguard-docs take to install?
- 45 minutes in the run that decided this verdict, from a clean machine to a running state. That is one measured attempt, not an average.
- Does wireguard-docs need a GPU?
- Not to start. Argusic reached a running state on a machine with no GPU.
- What goes wrong when installing wireguard-docs?
- 6 things broke in the recorded run, and 6 were fixed without human help. Each one, and the time it cost, is listed on this page.
- Where is the evidence for wireguard-docs?
- All 2 recorded runs are on this page, each linking to its full log and terminal recording, stored with a sha256 fingerprint so it cannot be quietly altered.